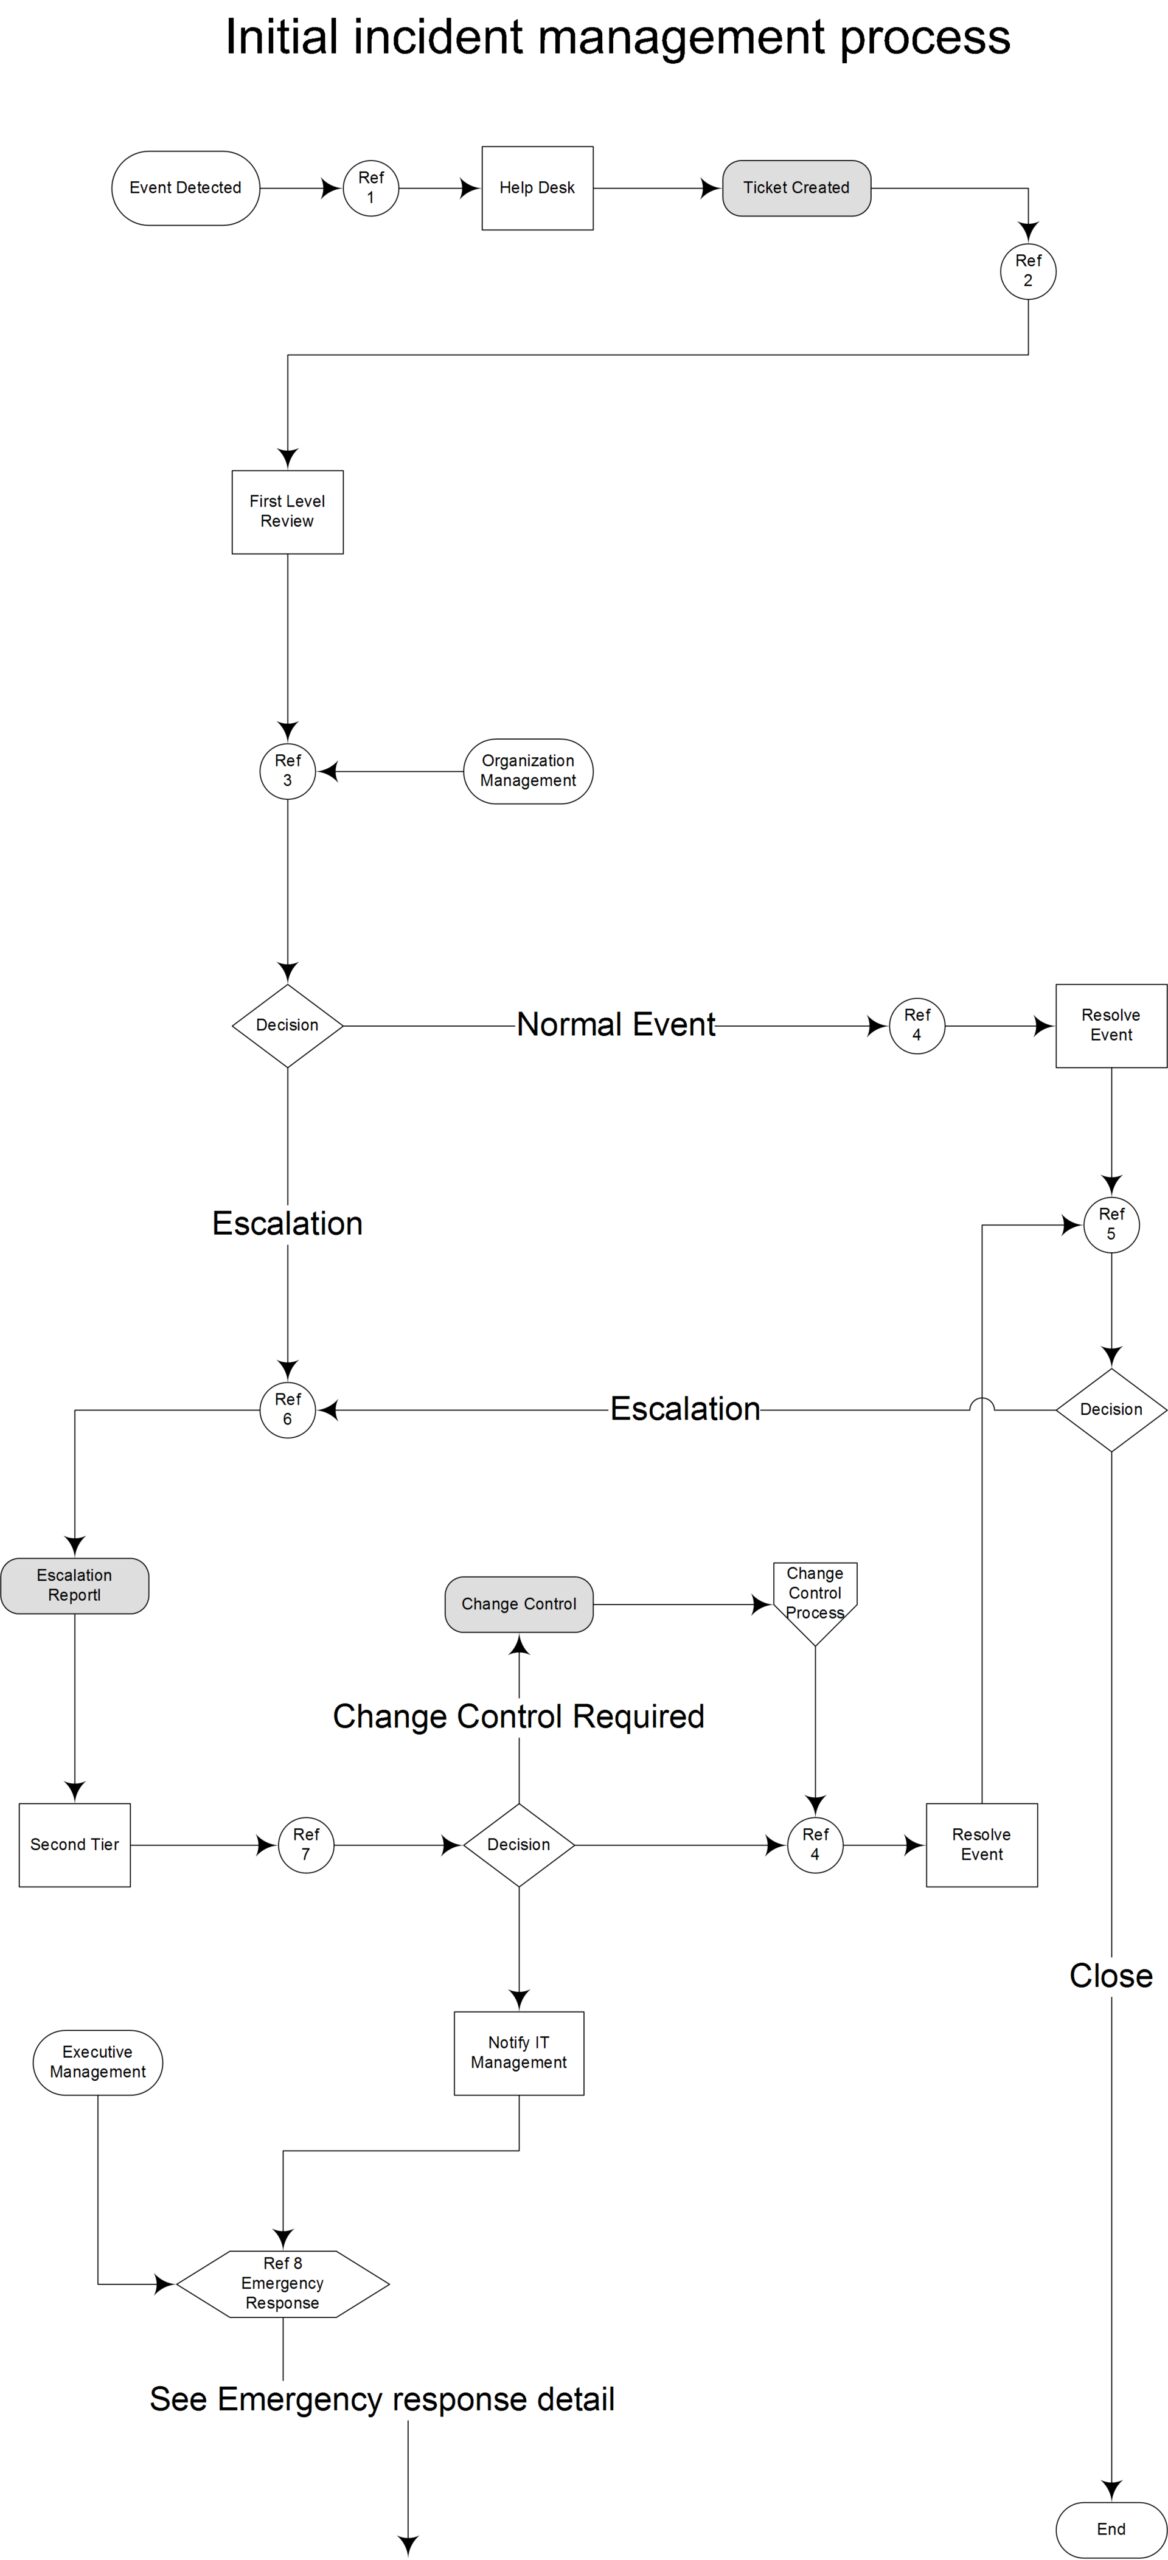
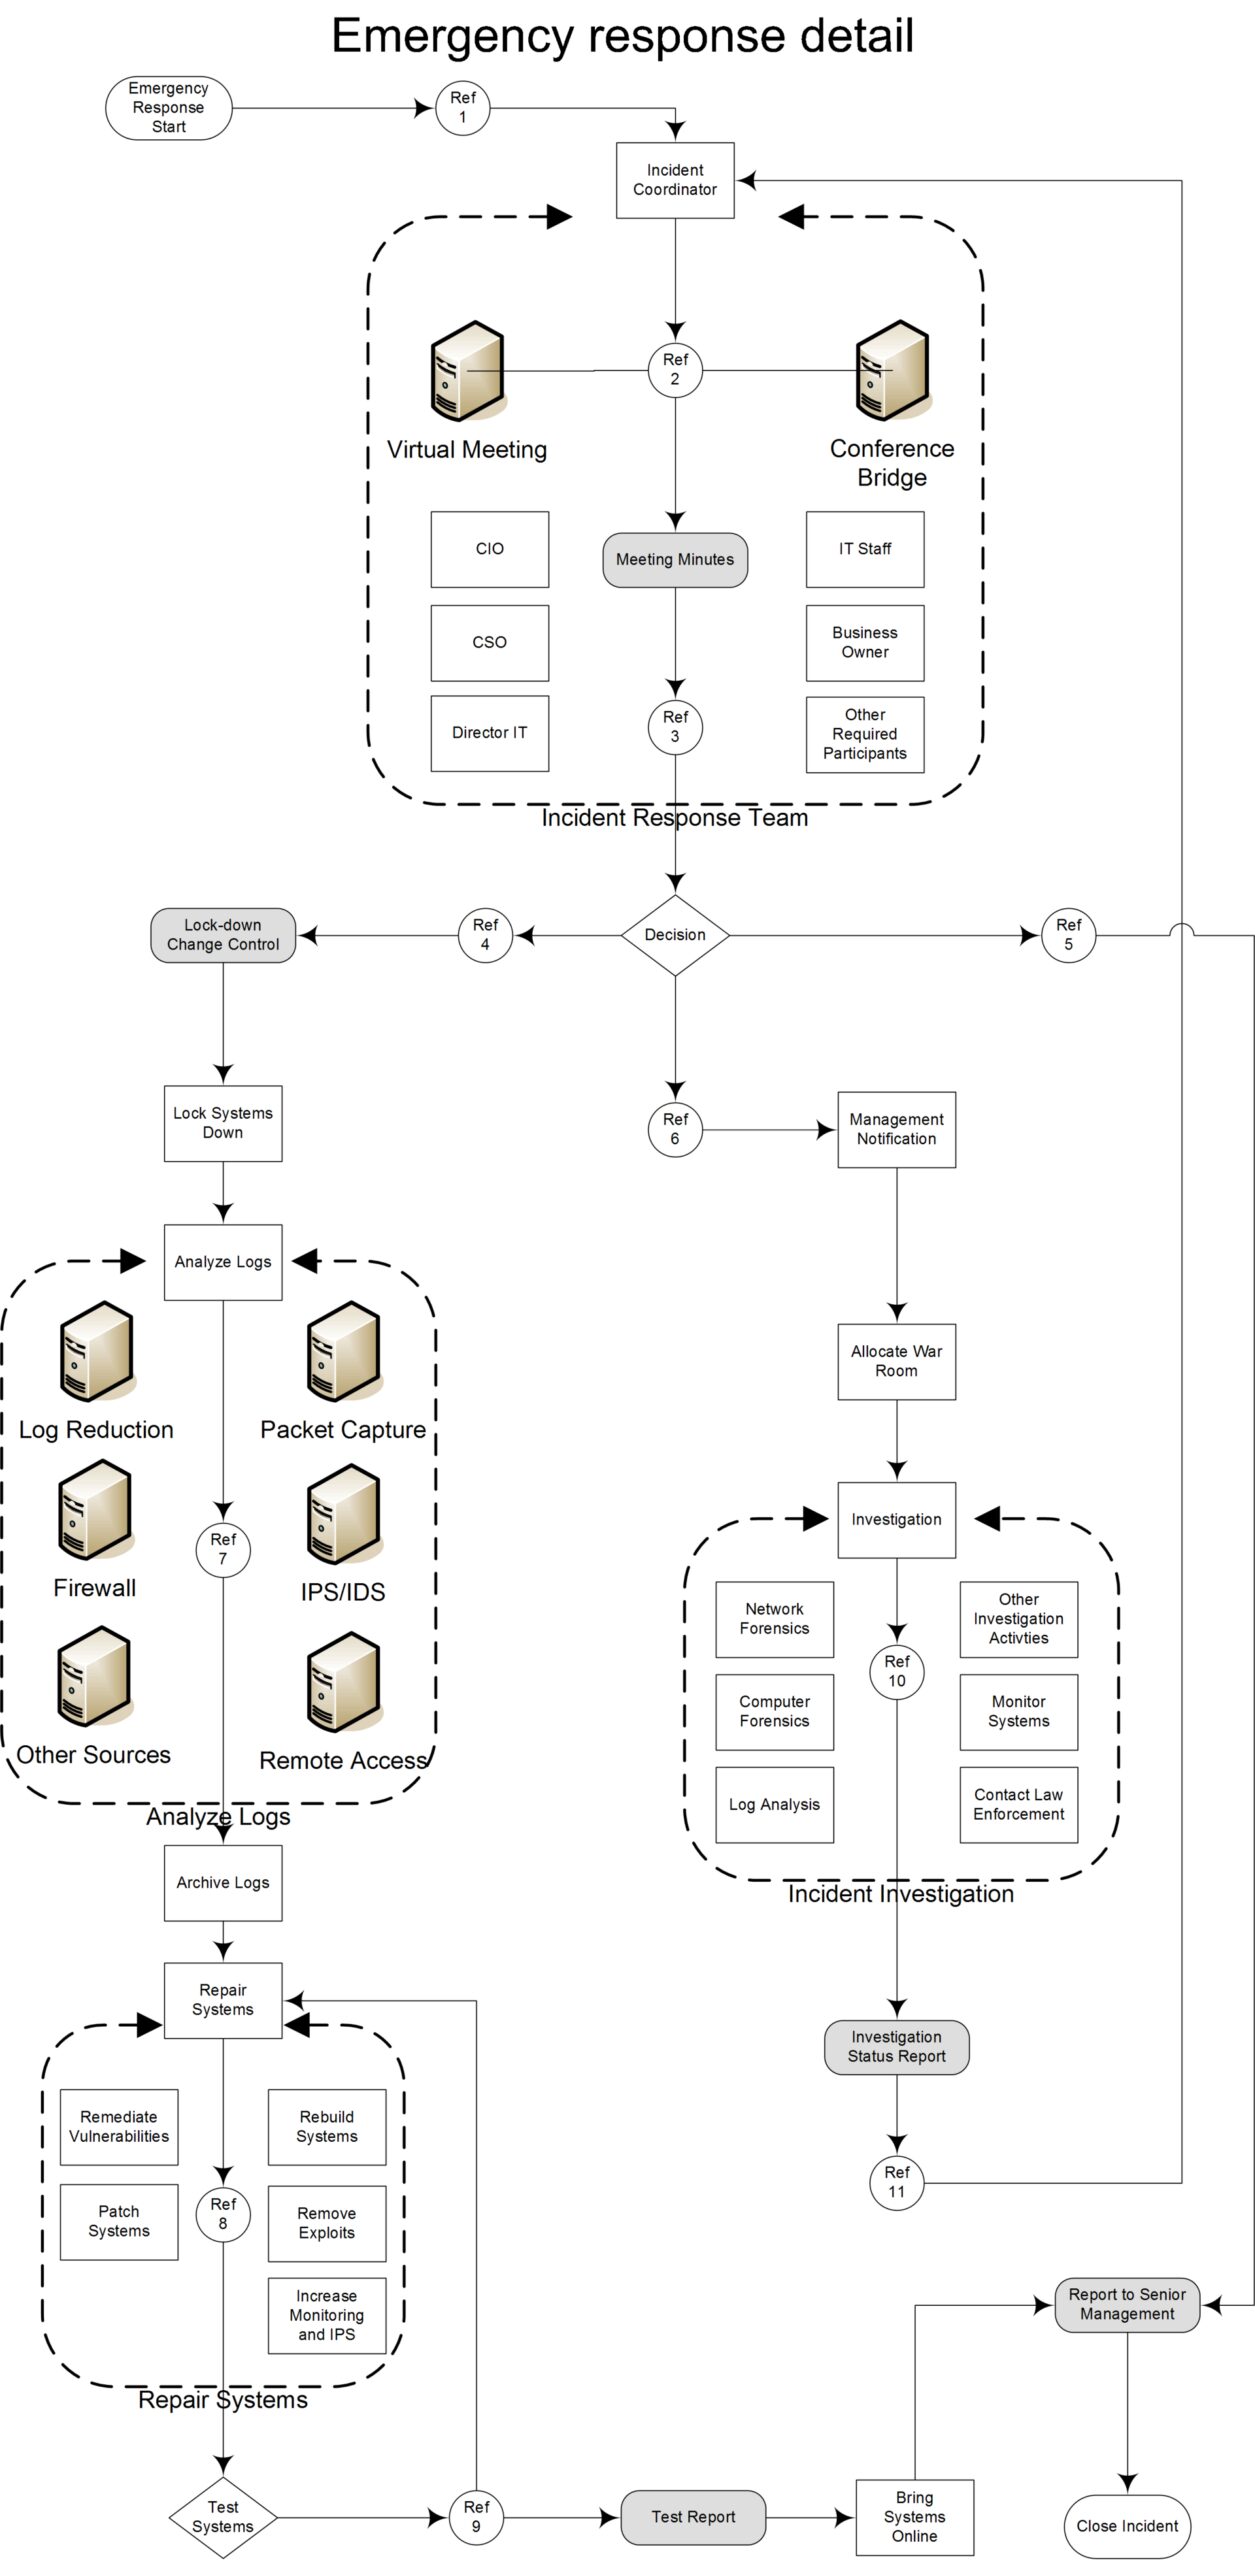
Most organizations have an incident response plan document sitting somewhere in a shared drive, and a surprising number of these plans have never been tested through a real, realistic exercise. A plan that exists purely on paper, untested, frequently fails in important ways precisely when it matters most – during a real, live security incident. … Read more
Software supply chain attacks – where attackers compromise a widely-used dependency to indirectly reach a much larger number of downstream targets – have grown into one of the more significant security concerns in recent years, and understanding the real risk helps organizations build appropriately proportionate, effective defenses against this specific, growing threat category. Why Supply … Read more
PCI DSS compliance is mandatory for any business handling payment card data, but the specific requirements and their real practical implementation can feel overwhelming for e-commerce businesses navigating this for the very first time. Understanding the actual core requirements and, importantly, what scoped compliance looks like helps demystify a process that often feels considerably more … Read more
Web application firewalls provide a valuable layer of defense for web applications, but organizations sometimes deploy them with an overly optimistic understanding of what they protect against, leading to genuine, real gaps in overall security posture when a WAF is treated as a comprehensive solution rather than one specific, valuable layer within a broader defense … Read more
Identity and access management misconfigurations in cloud environments consistently rank among the most serious, commonly exploited security findings, and privilege escalation – where an attacker with limited initial access finds a path to considerably broader permissions – is often the specific mechanism that turns a comparatively minor initial compromise into a major, full-scale breach. Why … Read more
Organizations invest heavily in technical security controls – firewalls, intrusion detection, endpoint protection – while social engineering attacks continue succeeding at a remarkable, persistent rate, bypassing all of that technical investment entirely by targeting people directly instead of any technical system. Understanding why social engineering remains so effective clarifies why technical defenses alone can never … Read more
Vulnerability management sounds conceptually straightforward – find vulnerabilities, fix them – but organizations consistently struggle to build effective programs at real scale, drowning in a sheer volume of scanner findings without a clear, defensible process for prioritizing which ones matter most and deserve real, prompt attention. Why Raw Vulnerability Counts Are Misleading A typical vulnerability … Read more
Container escape vulnerabilities – flaws that let an attacker break out of a container’s intended isolation boundary and access the underlying host system – represent one of the more serious, high-impact vulnerability classes in containerized environments. Understanding how these work, and what mitigates the real risk, matters for anyone running production containerized workloads at any … Read more
Hardcoded credentials – API keys, passwords, and tokens embedded directly in source code rather than properly managed through a dedicated secrets management system – remain a persistent, common security finding despite being a well-understood risk for years. Understanding why this keeps happening, and how to address it systematically, matters for any organization with a real, … Read more
Ransomware incidents unfold with a speed and disorientation that no amount of reading about them ever fully prepares an organization for. The decisions made in the first 24 hours meaningfully shape the entire trajectory of recovery. A clear, pre-planned response reduces both the real chaos and the actual damage considerably compared to organizations improvising their … Read more