Vulnerability management sounds conceptually straightforward – find vulnerabilities, fix them – but organizations consistently struggle to build effective programs at real scale, drowning in a sheer volume of scanner findings without a clear, defensible process for prioritizing which ones matter most and deserve real, prompt attention. Why Raw Vulnerability Counts Are Misleading A typical vulnerability … Read more
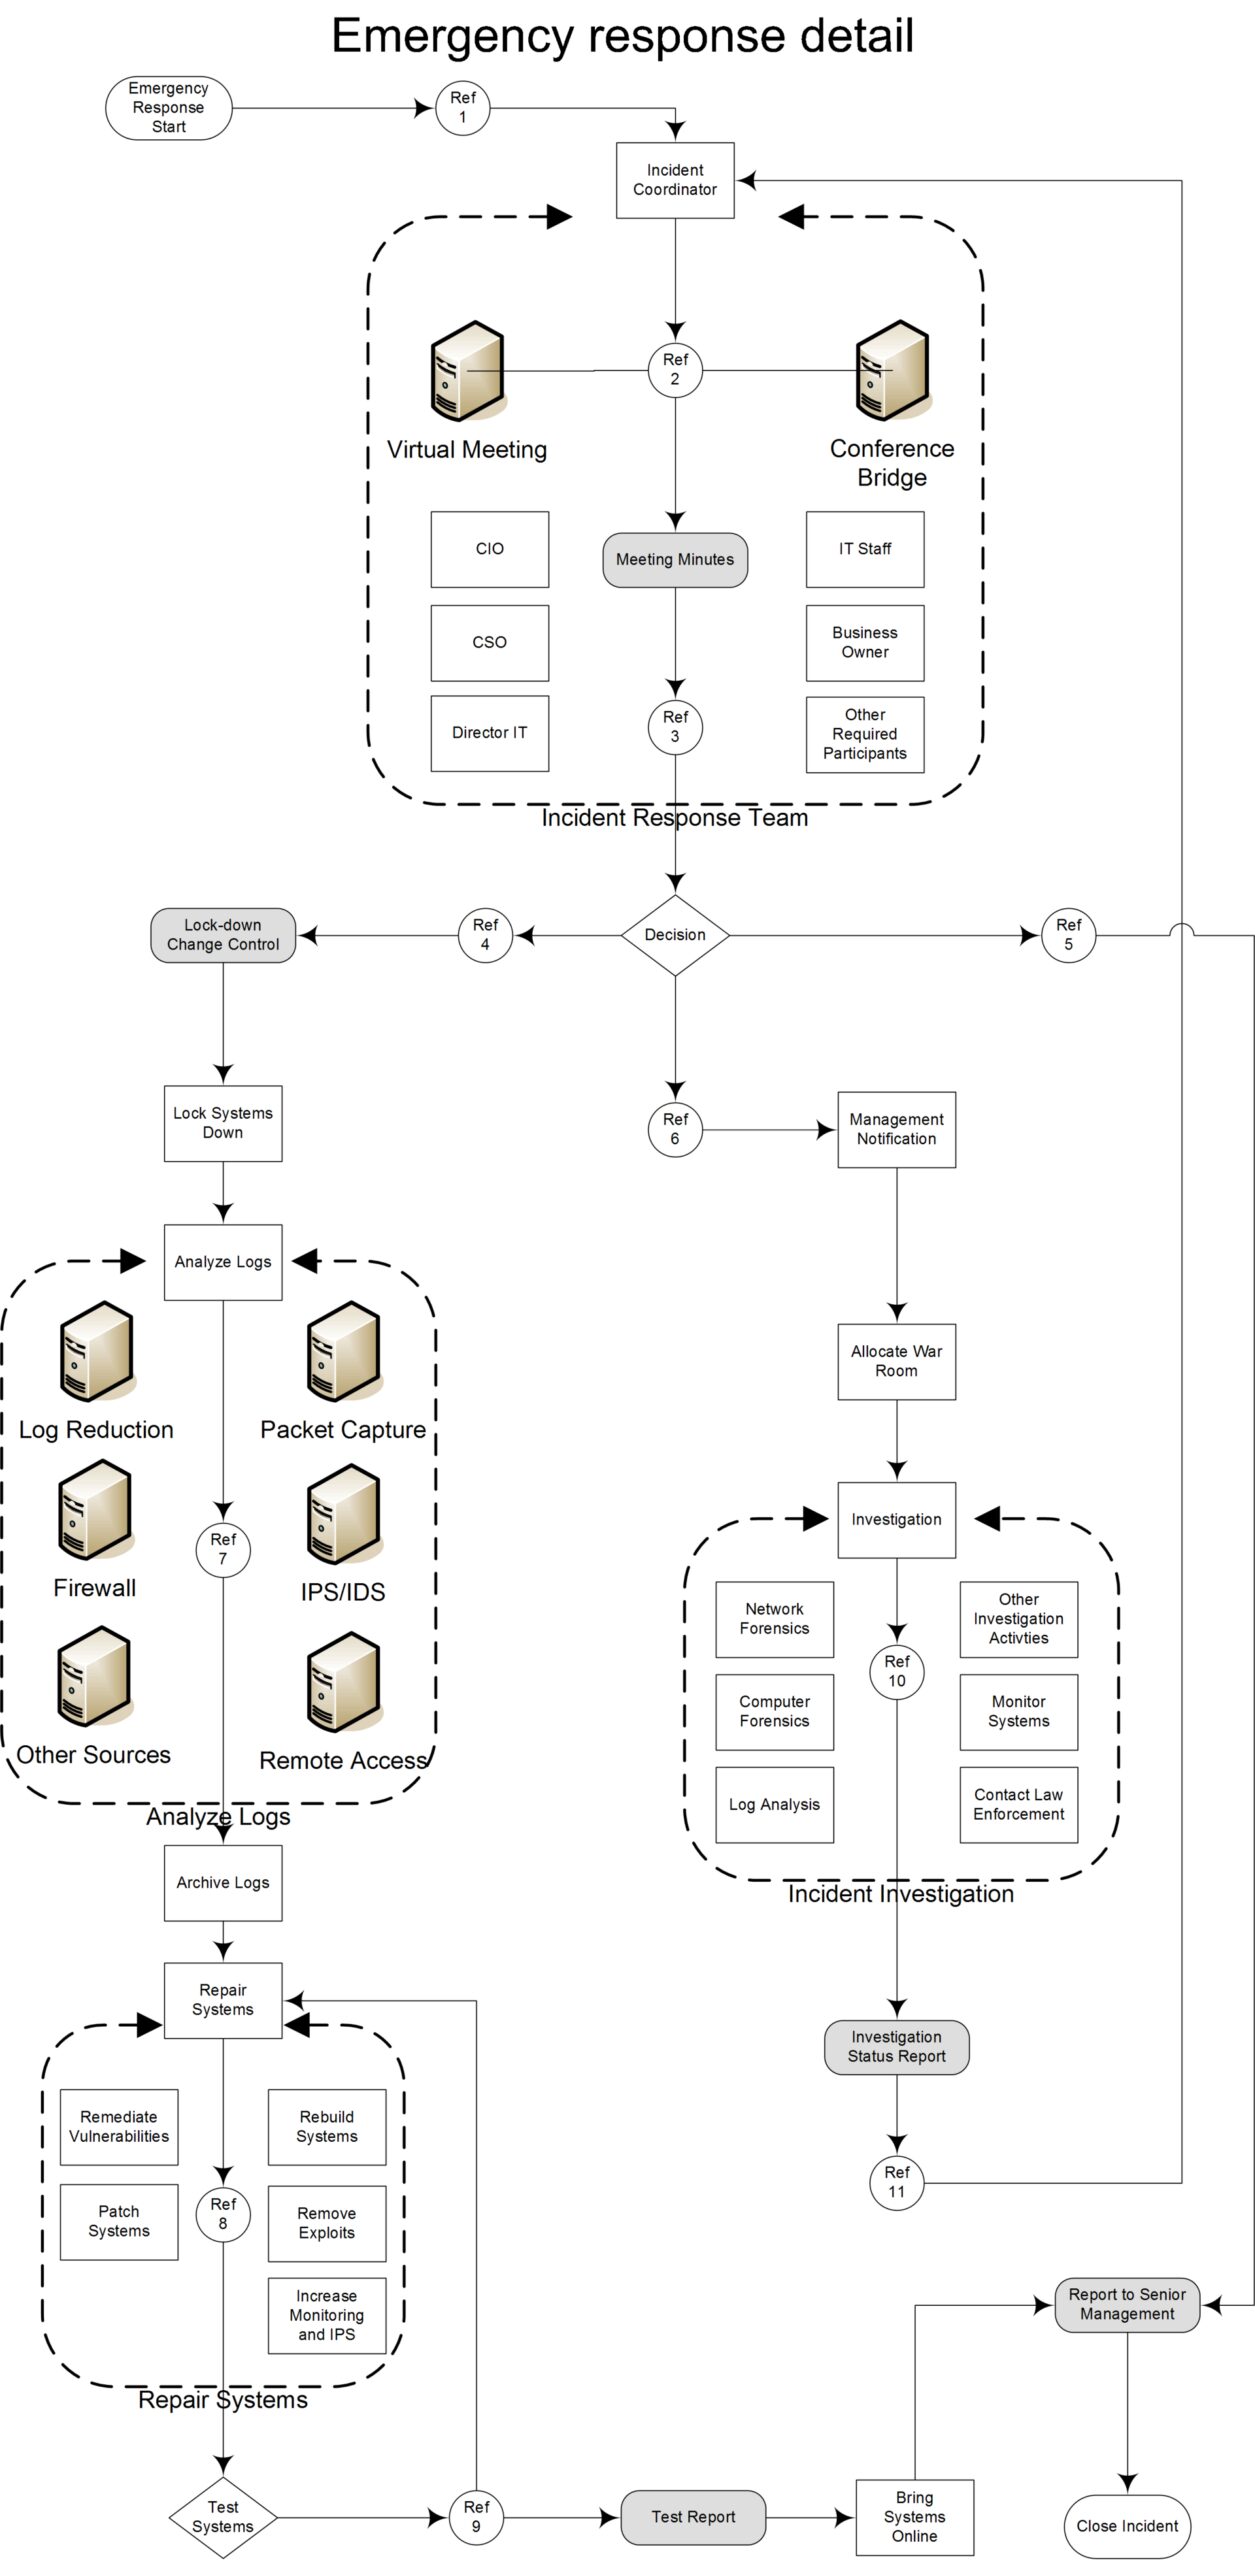
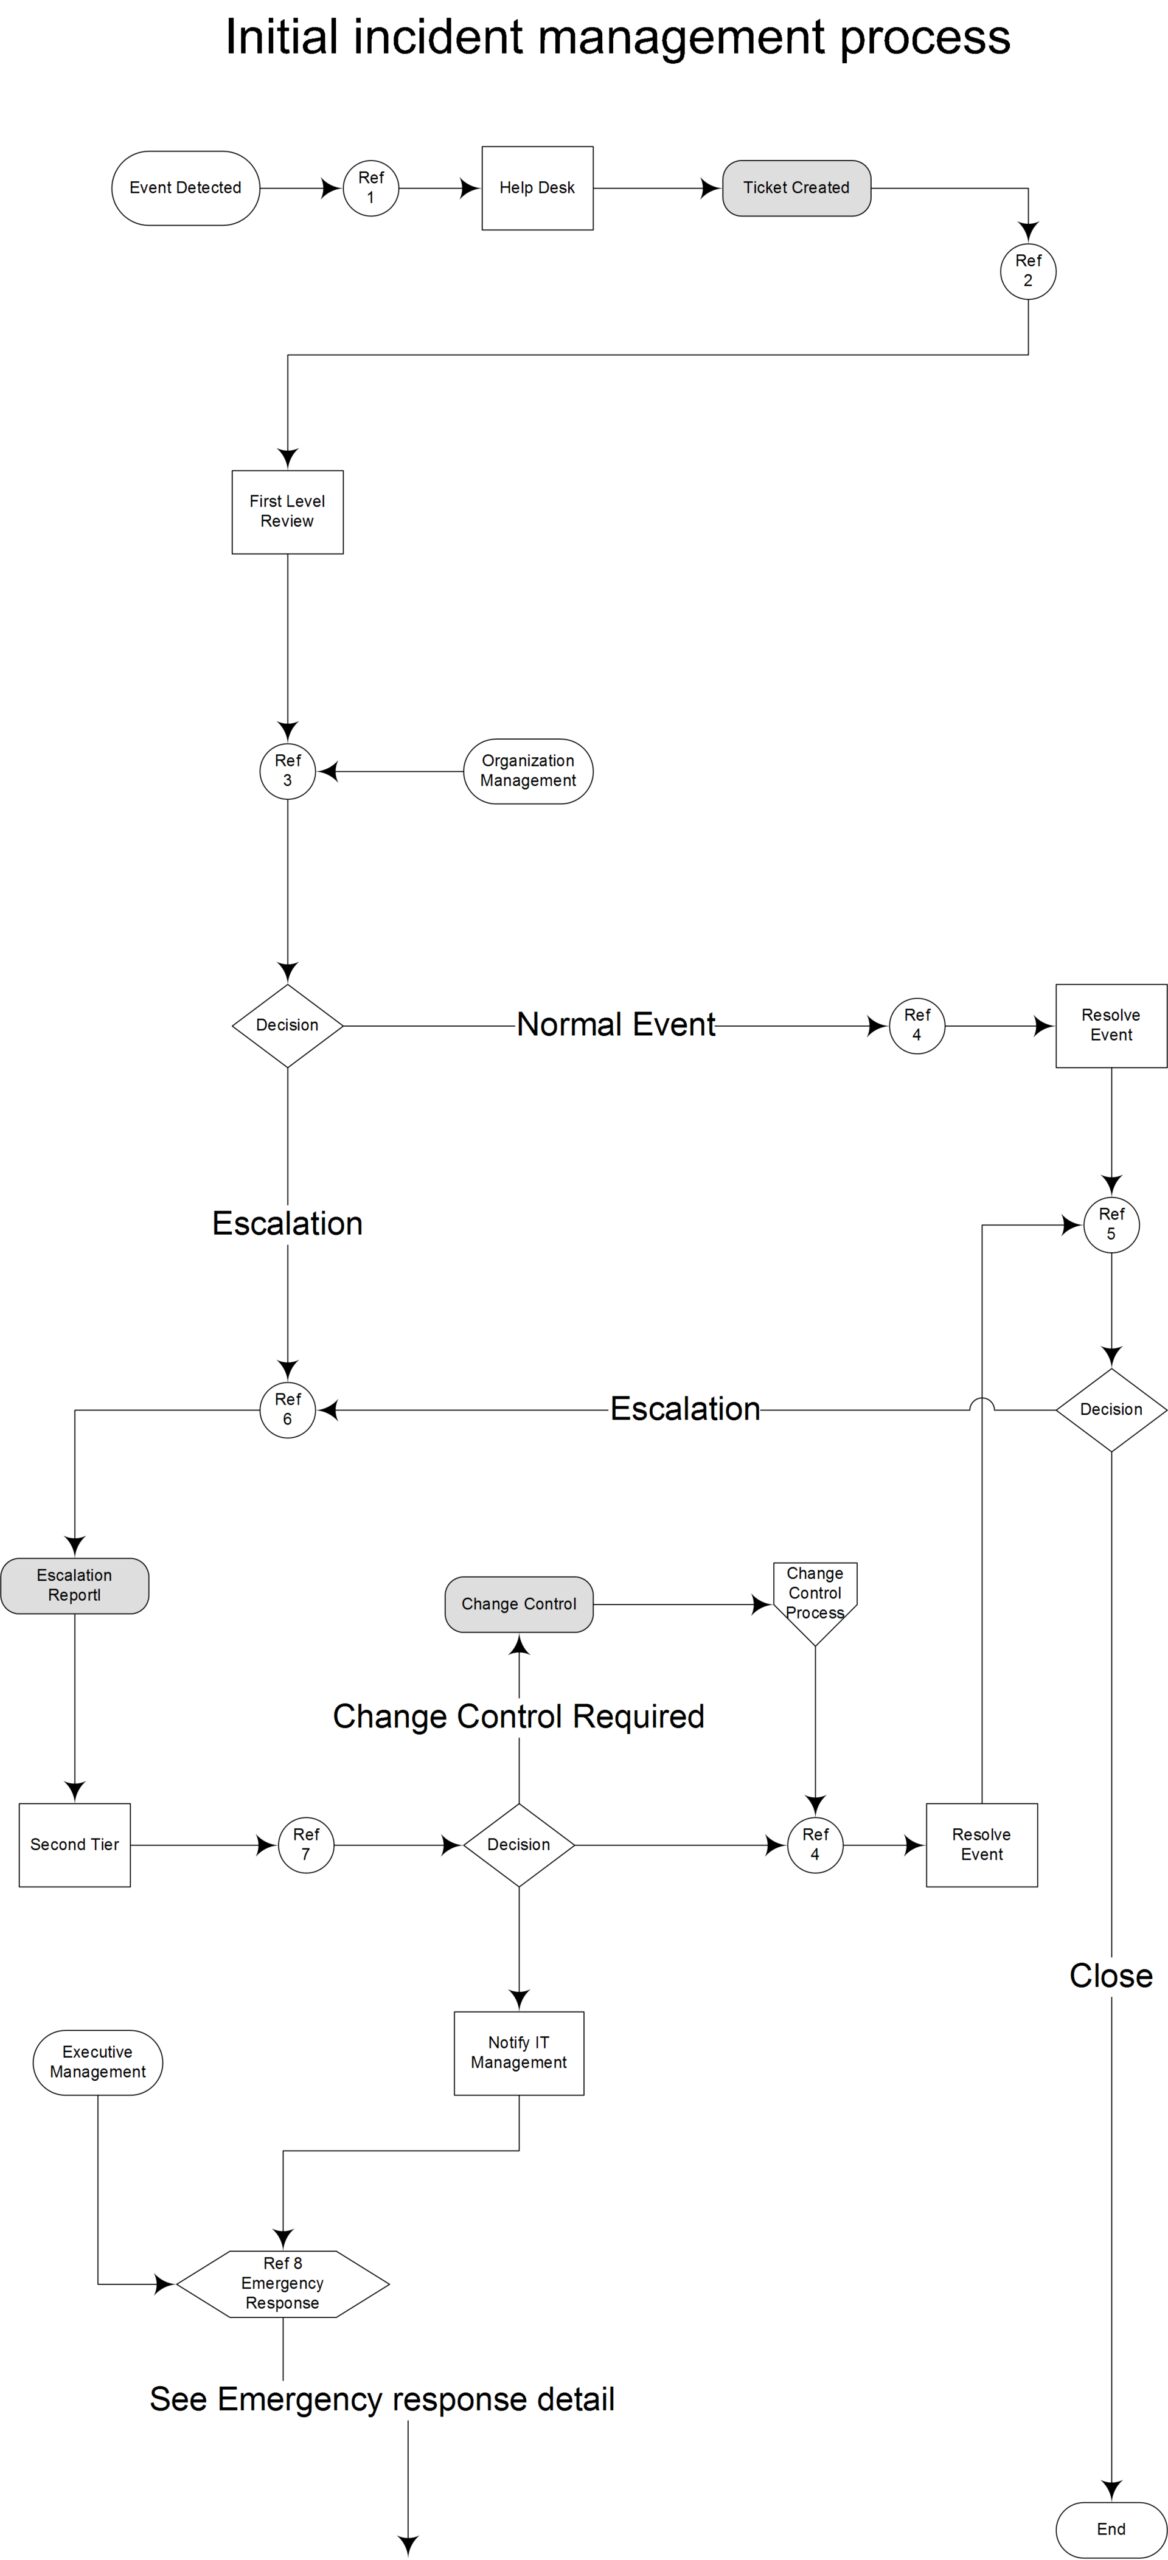
Ransomware incidents unfold with a speed and disorientation that no amount of reading about them ever fully prepares an organization for. The decisions made in the first 24 hours meaningfully shape the entire trajectory of recovery. A clear, pre-planned response reduces both the real chaos and the actual damage considerably compared to organizations improvising their … Read more
Ask a business owner what a “security assessment” involves and you will usually get a vague answer about scanning for vulnerabilities. That is part of it, but a thorough assessment covers far more ground than an automated scanner report – and the gap between a real assessment and a superficial one is exactly where the … Read more
A company discovers a leaked API key during a routine security review, rotates it within the hour, and treats the incident as genuinely closed – until a follow-up investigation reveals that key had been embedded in a genuinely large number of downstream integrations and cached configurations, several of which quietly broke the moment rotation happened, … Read more